After a Ransomware Attack on Your Server, Avoid These 5 Mistakes: Preserve the Scene to Recover Databases and Virtual Machines
When a corporate server is hit by ransomware, the greatest loss often comes not from the encryption itself but from panicked reboots, antivirus scans, forced database mounts, and in-place backup restores. This article breaks down the five most destructive actions to avoid after a server infection and provides a standard self-rescue path from freezing the scene and identifying the ransomware family to data recovery and hardening.
Ransomware Mutating Again? Don't Panic—Take Control Against 'Unstoppable' Attacks
Ransomware evolves rapidly, and conventional defenses often fall short. In the face of sudden attacks, enterprises should break free from the 'passive antivirus' mindset and adopt a 'closed-loop protection' strategy that includes emergency response, data recovery, and deep security hardening.
How to Investigate a Ransomware Extension Added to Your Files: Don’t Just Look at the Last Few Letters—Follow These Three Steps to Identify the Family
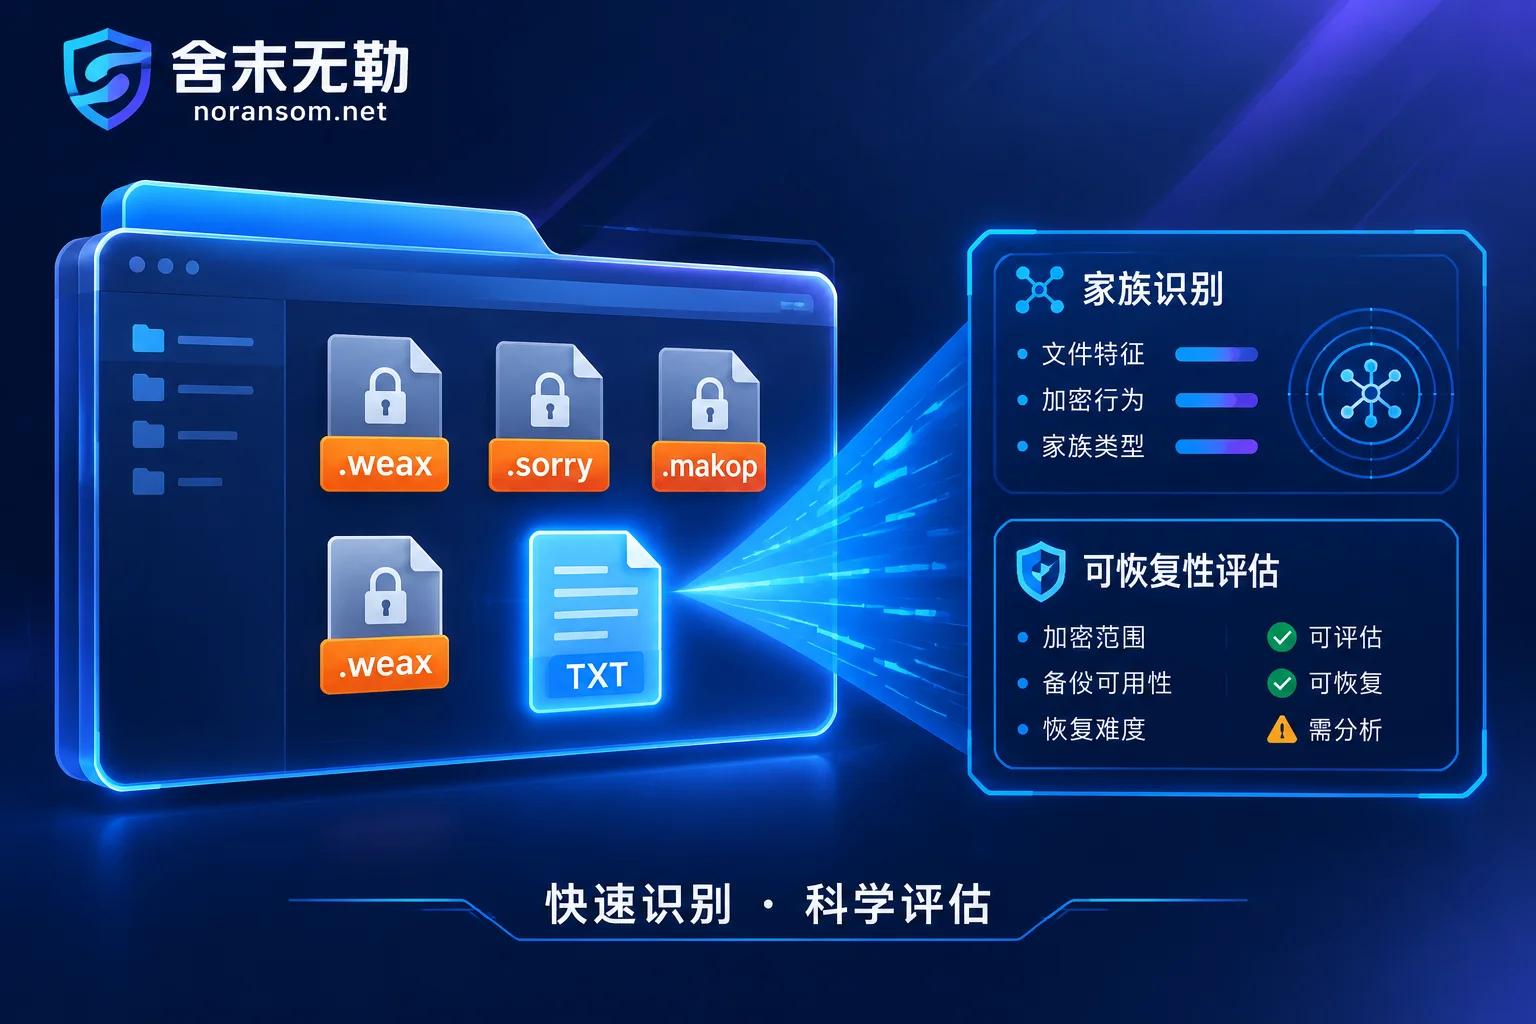
When files on your server or computer are appended with an unfamiliar ransomware extension, renaming them or blindly running generic decryption tools found online often destroys the originals. This article, based on the characteristics of recently active families such as Weaxor (.weax/.rox), Sorry (.sorry/.ths), and Makop, explains how to accurately identify the ransomware family through extension structure, ransom notes, and underlying file features, and provides a practical path for assessing the recoverability of databases, ERP, and virtualized environments.
How to Recover a SQL Server Database Encrypted by Ransomware: Don't Force-Attach MDF, Evaluate Recovery Chances in Three Steps
When a SQL Server database (MDF, NDF, BAK) is encrypted by ransomware, blindly running DBCC CHECKDB or forcing attachment can cause further damage. This article explains emergency actions, page-level recovery principles, and how to assess ransomware data recovery feasibility without paying the ransom.
Can Files Encrypted with .AIR Be Saved? First Distinguish Makop from Dharma, Then Decide on Ransomware Decryption and Recovery
When server, ERP, or database files are renamed with .AIR or .air extensions, do not blindly apply decryption tools. The same extension may belong to the Makop family or a Dharma (CrySiS) variant. This article explains how to distinguish the families by file naming structure and ransom note characteristics, outlines on-site containment, and details underlying data recovery paths for SQL Server and business systems like Kingdee and Yonyou when direct decryption is blocked.