How to Investigate a Ransomware Extension Added to Your Files: Don’t Just Look at the Last Few Letters—Follow These Three Steps to Identify the Family
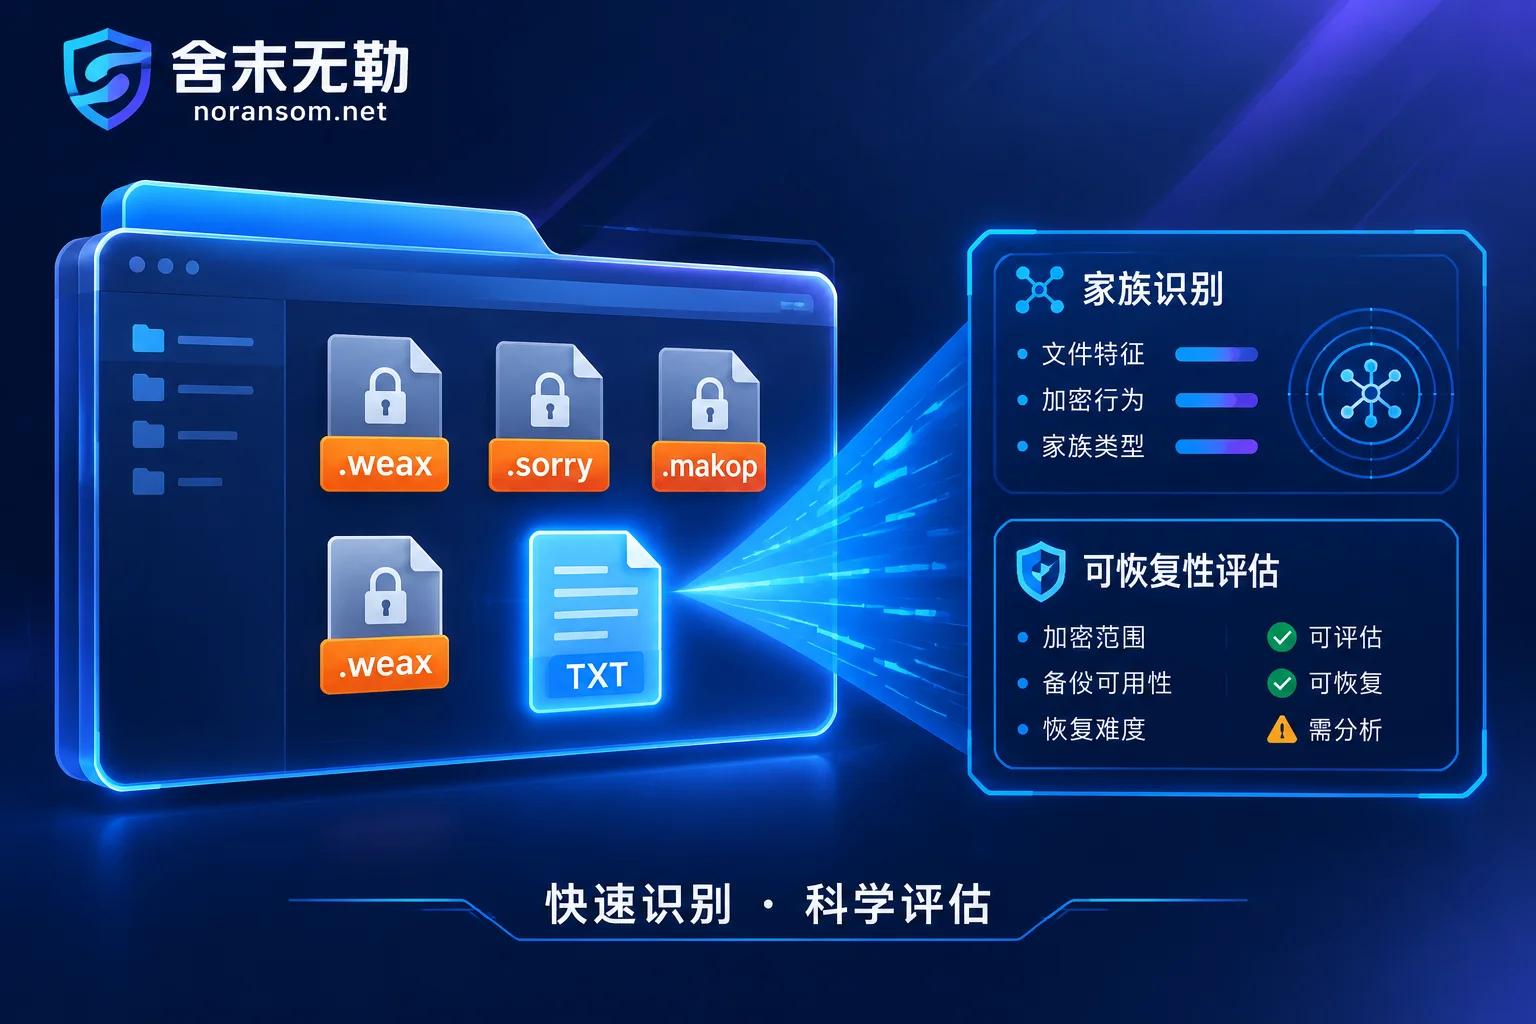
When files on your server or computer are appended with an unfamiliar ransomware extension, renaming them or blindly running generic decryption tools found online often destroys the originals. This article, based on the characteristics of recently active families such as Weaxor (.weax/.rox), Sorry (.sorry/.ths), and Makop, explains how to accurately identify the ransomware family through extension structure, ransom notes, and underlying file features, and provides a practical path for assessing the recoverability of databases, ERP, and virtualized environments.