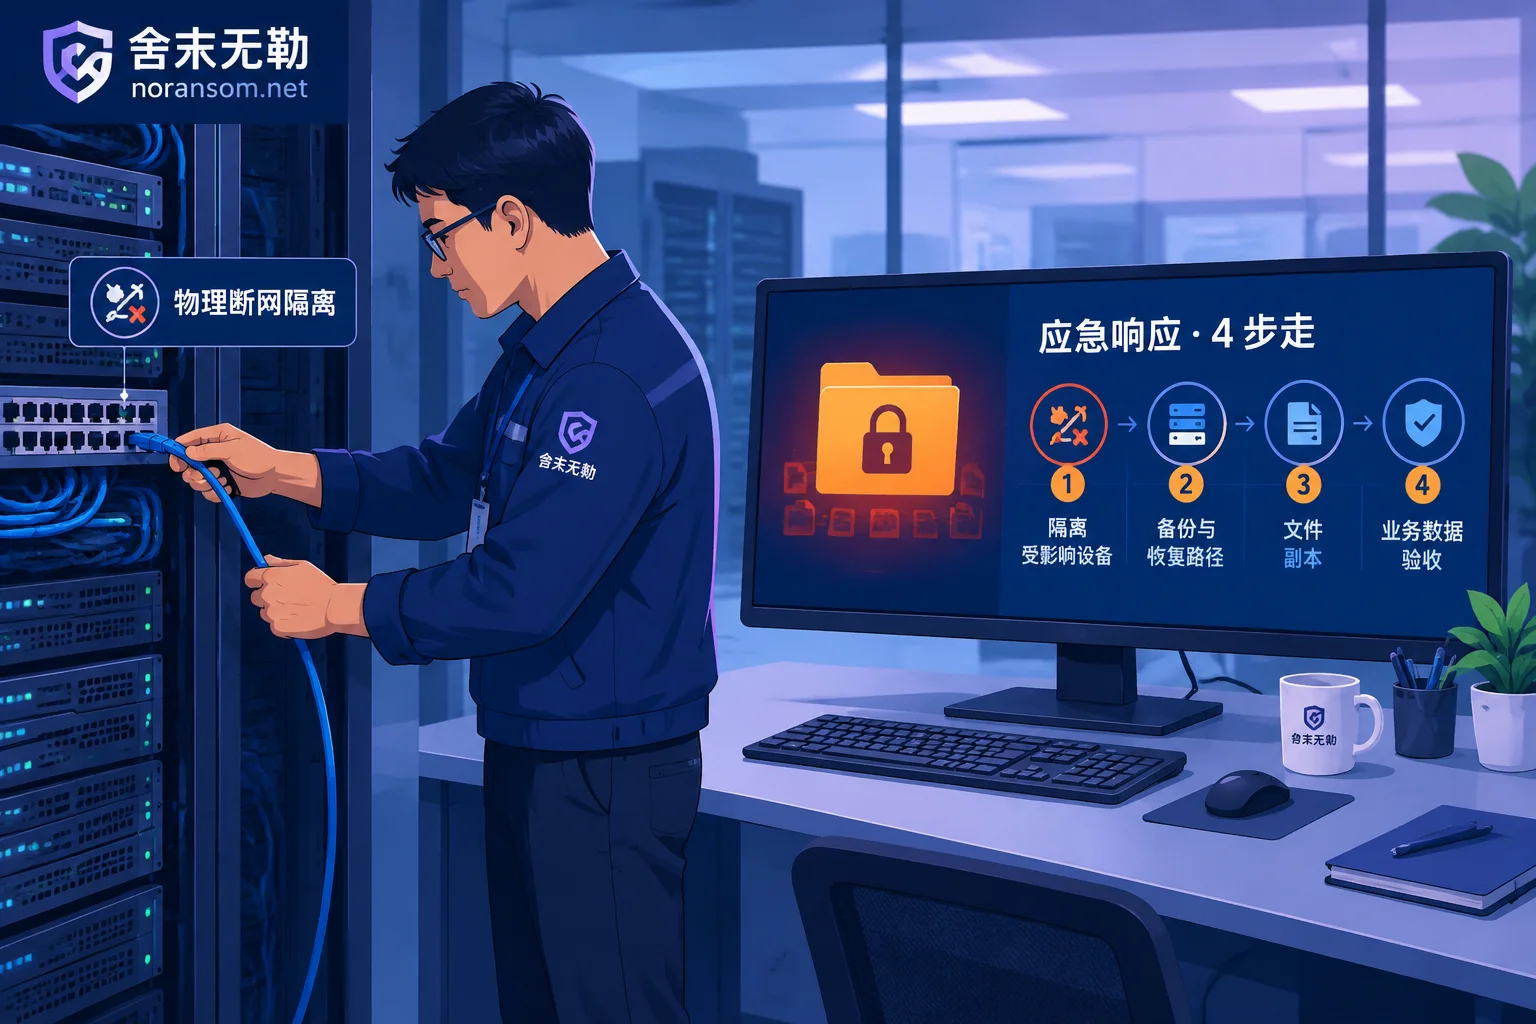
What to Do If You're Hit by Ransomware: A Complete Emergency Decision Checklist from the First 30 Minutes of Loss Control to Business Restoration
After discovering that your computer or server has been encrypted by ransomware, blindly restarting, running antivirus scans, or contacting the hackers often reduces the originally available data recovery space. This article is aimed at business leaders and IT operations staff, outlining a four-step standardized emergency response process: isolating the network and preserving the scene within the first 30 minutes, identifying the ransomware family, choosing between decryption and data extraction paths, and eradicating backdoors to rebuild defenses after cleanup.
Why Ransomware Victims Get Encrypted Again After Data Recovery: Recovering Data Is Only the First Step—Don't Go Live Until These Four Backdoors Are Cl
Many enterprises hit by Weaxor, Mallox, or Sorry ransomware painstakingly roll back from backups or finish database repairs, only to be re-encrypted within hours of going live. This article breaks down the four hidden causes of secondary infections (infected backups, unclosed initial entry points, persistent privileges, and internal lateral-movement jump hosts) and provides a complete pre-launch checklist for a safe return to production after recovery.
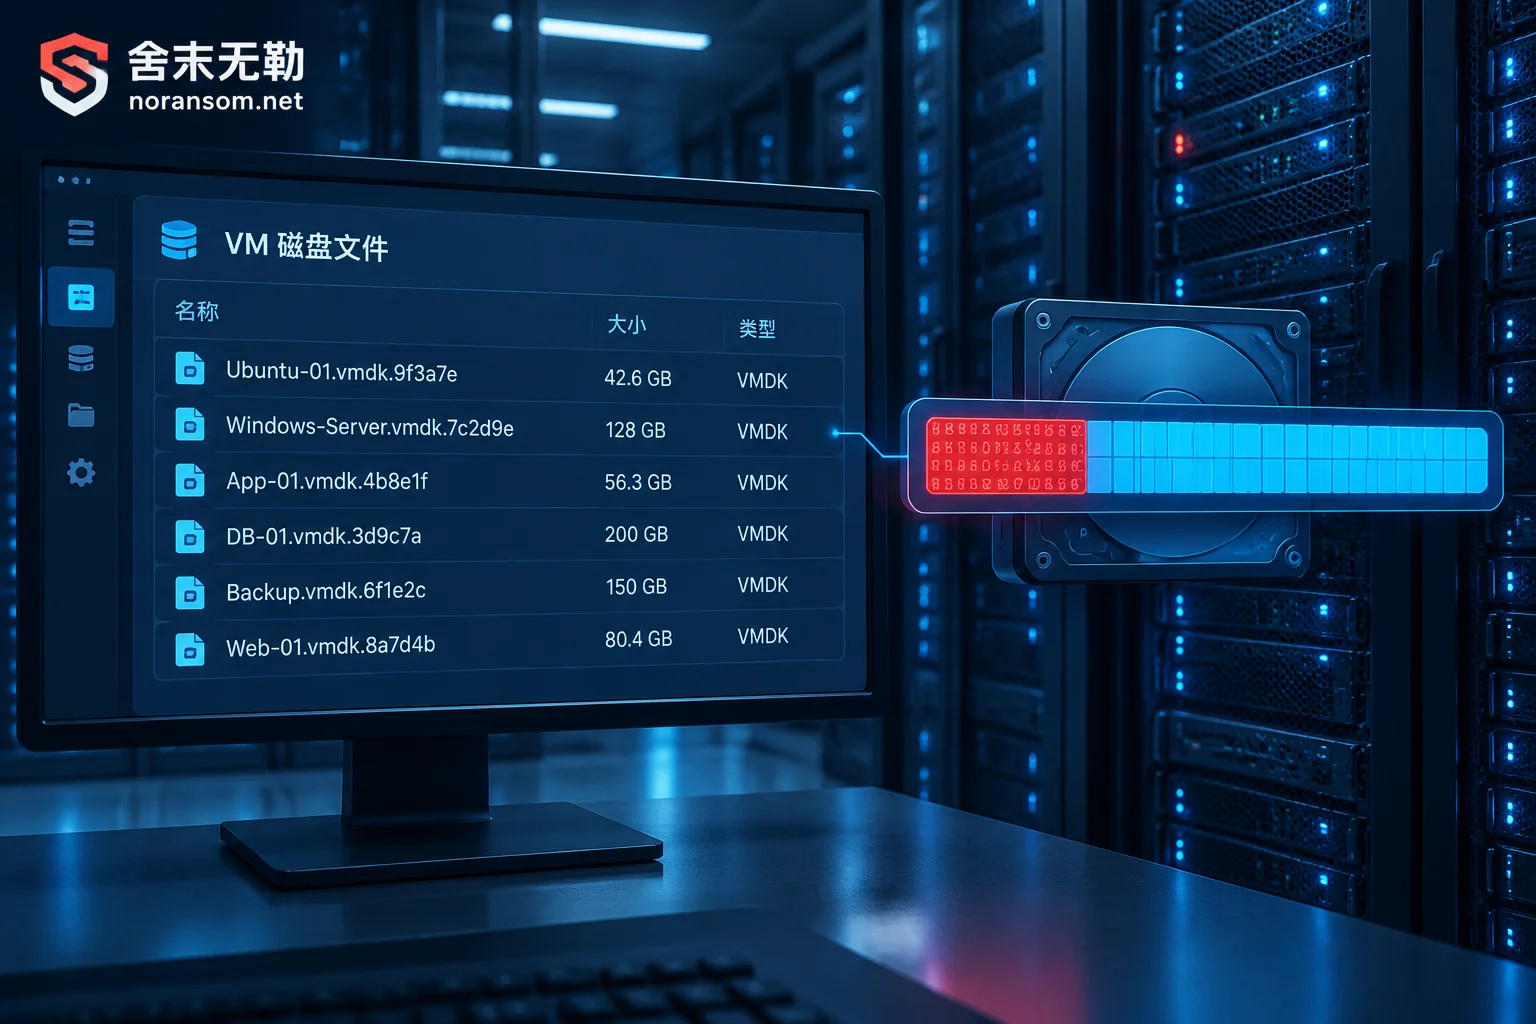
Can Data Be Extracted from an Encrypted VMDK File? It Depends on How Much of the Flat Volume Is Overwritten
A virtual machine failing to boot does not mean all data is encrypted. This article explains the order for judging extractability after a VMDK is encrypted by ransomware: first isolate and make a read-only clone, then distinguish whether only the descriptor is encrypted, the flat volume header/intermittent encryption, or full-disk continuous encryption, and provides corresponding extraction paths, prohibited operations, and verification methods.
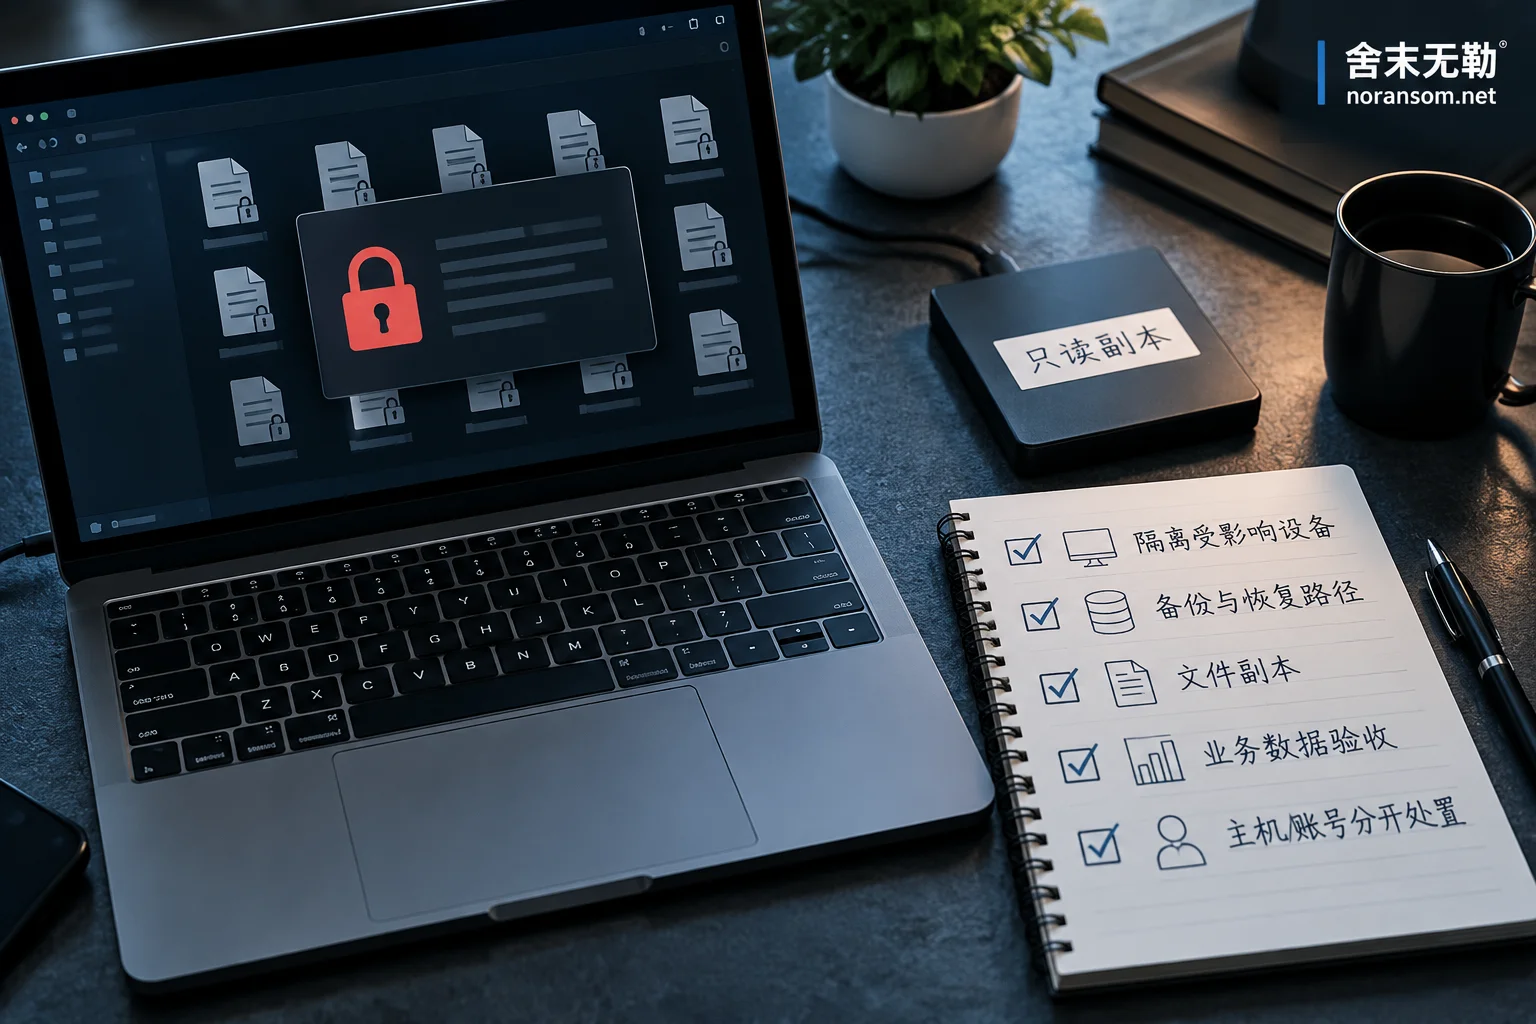
What to Prepare Before Contacting a Ransomware Recovery Company
Ransomware recovery cannot be priced from a single statement that files were encrypted. This article explains the five types of materials usually needed before assessment and quotation: the original ransom note, a few small non-sensitive encrypted samples with unencrypted counterparts, the affected asset and database environment, backup and snapshot status, actions already taken after the incident, and how to sample without causing secondary damage or leaking sensitive data.
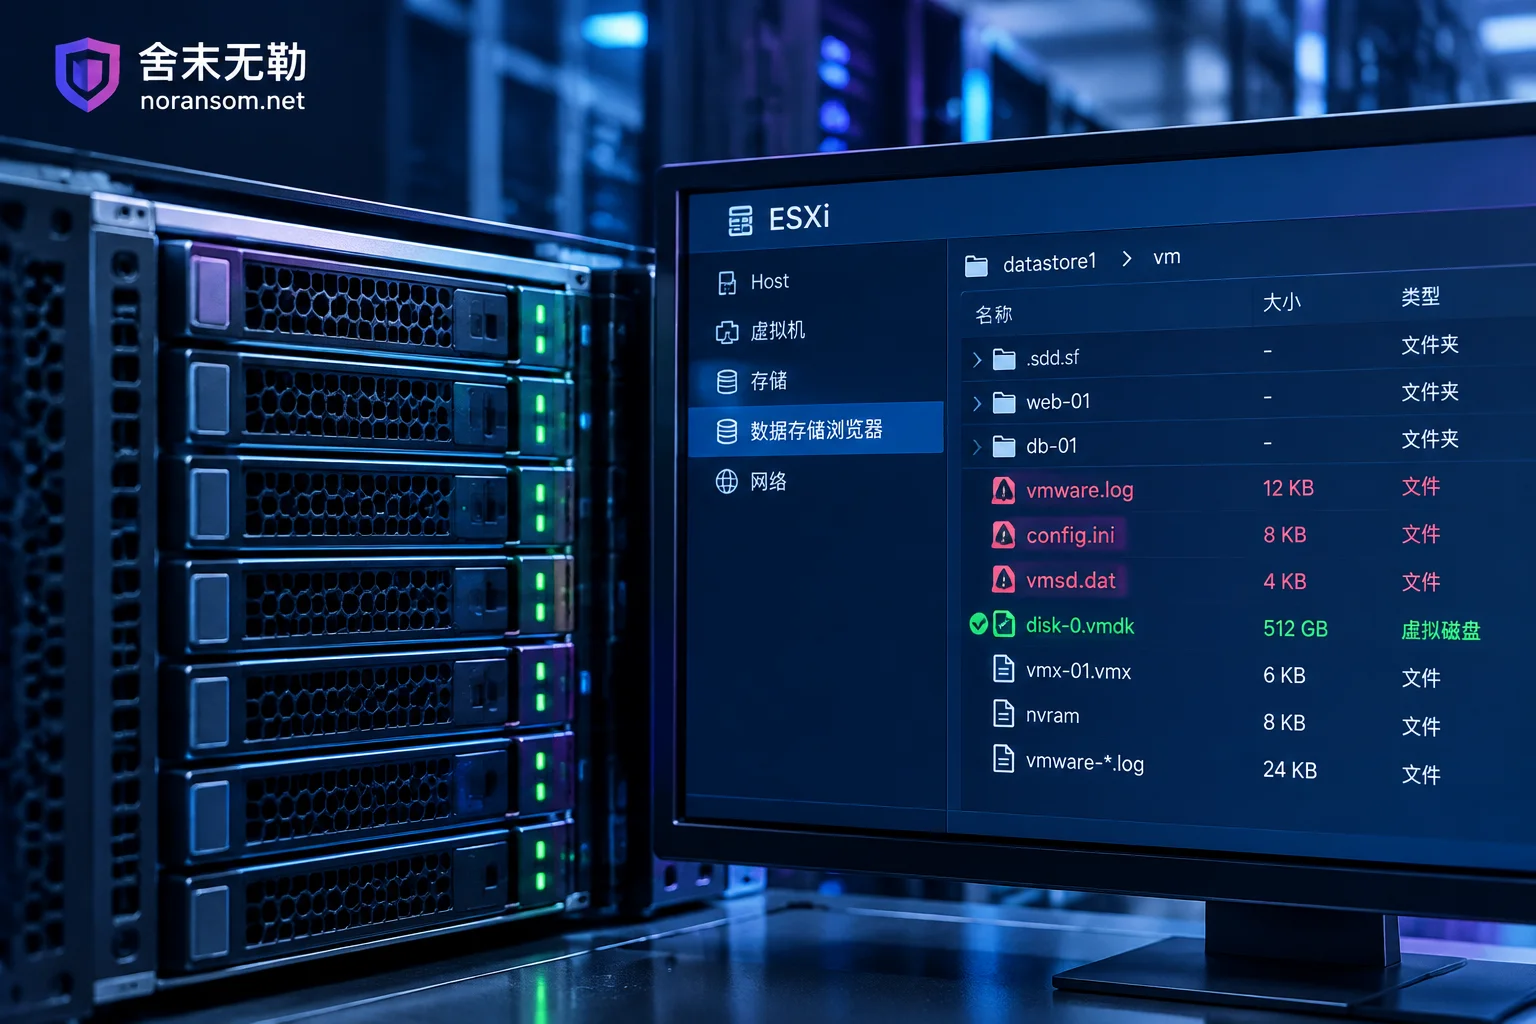
ESXi VM Encrypted with No Snapshot: Don't Touch the Original Storage—Assess What's Recoverable in This Order
When an ESXi VM is encrypted by ransomware with no snapshot or usable backup, first stop all writes to the datastore, then determine whether the VM config files or the underlying -flat.vmdk data disks are damaged.


