只是一个默认分类
Ransomware Without a Free Decryptor: Can You Still Recover Data?
A missing free decryptor doesn't mean your data is gone. This article explains where free tools come from, why many variants lack them, and the recovery paths that don't require decryption—plus the dangerous actions that will destroy your chances.
Finance Computer Infected with Silver Fox Trojan: What to Do About Online Banking — Cut Off Fund Channels First, Then Discuss Removal
If a finance computer is suspected of Silver Fox remote access trojan infection, the first step is not antivirus scanning but unplugging USB shields, disconnecting from the network, switching to a clean device to check transactions and contact the bank to stop payments.
Ransomware Infection Already Rebooted: What to Do Now and What Recovery Options Remain
The machine has been rebooted, so in-memory traces and temporary keys are gone, but that doesn't mean all recovery paths are closed. This article explains the first isolation steps after a reboot, how to decide whether to power off again, why the original disk must be imaged first, and how to identify the family, inventory backups, and handle compromised credentials.
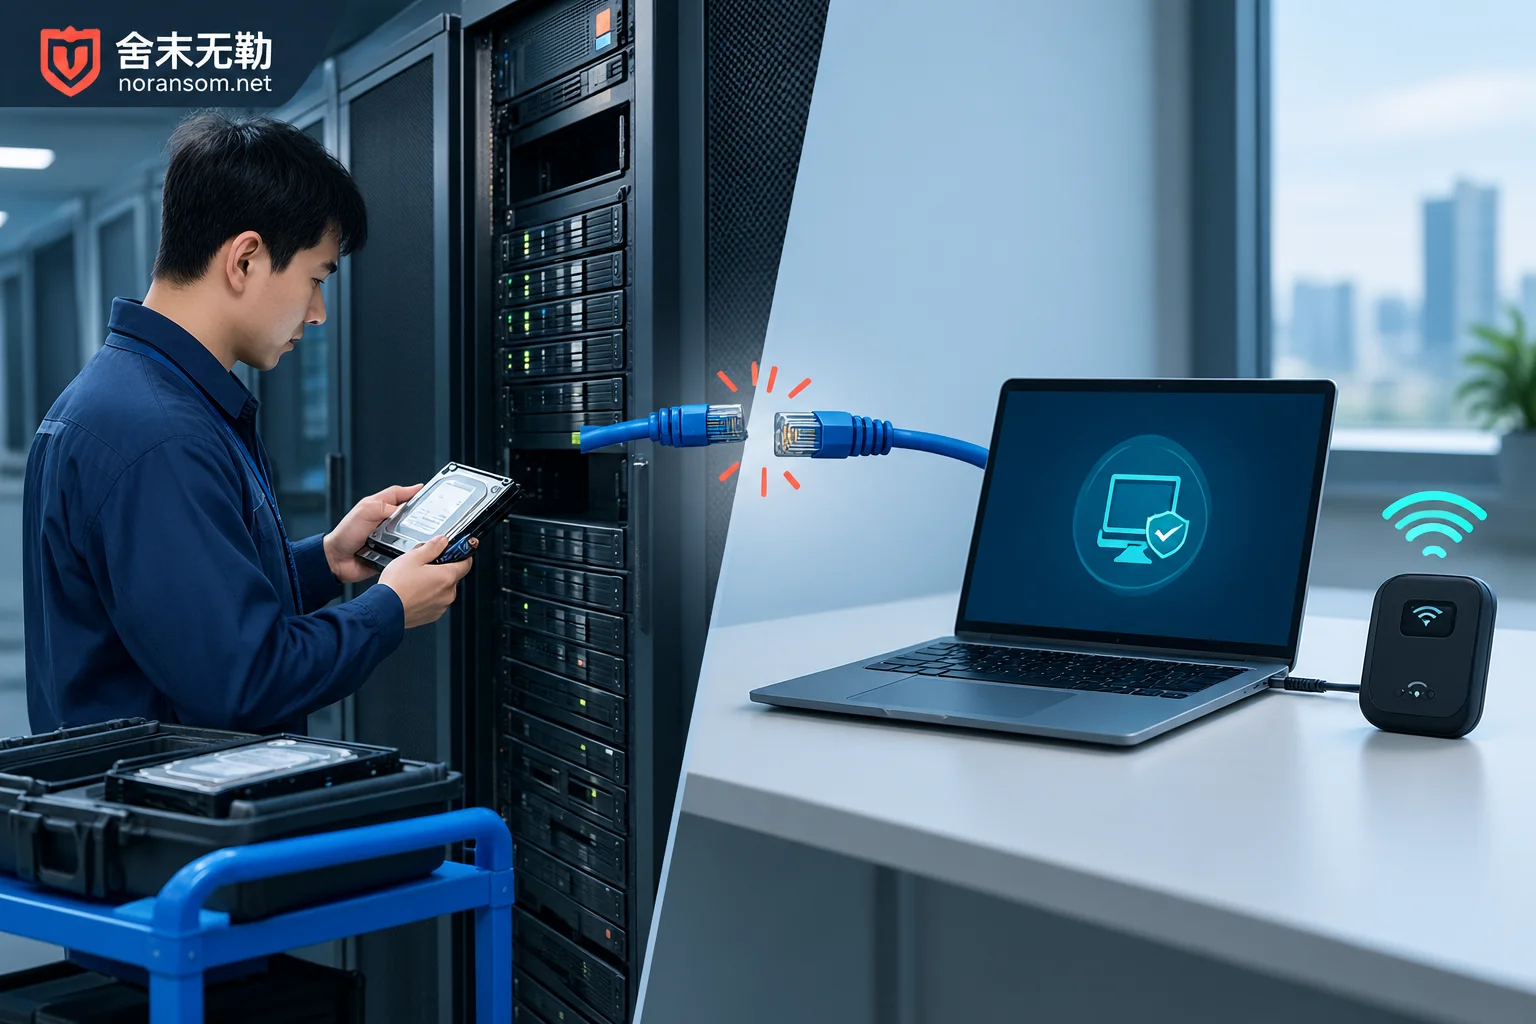
Ransomware: On-Site vs. Remote Response — How to Choose
Most ransomware incidents start with remote assessment; on-site response is required for physical media, very large data volumes, hardware faults, or forensic preservation.
Can an Encrypted SQL Server MDF Still Be Recovered? First See How Much Encryption Covers, Then Decide Your Path
After ransomware encrypts an MDF, recovery depends mainly on how much of the file is encrypted, whether usable backups exist, and whether further damage occurs afterward. This article gives priority actions, methods to judge three encryption coverage scenarios, a ranked list of four recovery paths, and the operations most likely to destroy data.


