只是一个默认分类
Can Files Encrypted with .AIR Be Saved? First Distinguish Makop from Dharma, Then Decide on Ransomware Decryption and Recovery
When server, ERP, or database files are renamed with .AIR or .air extensions, do not blindly apply decryption tools. The same extension may belong to the Makop family or a Dharma (CrySiS) variant. This article explains how to distinguish the families by file naming structure and ransom note characteristics, outlines on-site containment, and details underlying data recovery paths for SQL Server and business systems like Kingdee and Yonyou when direct decryption is blocked.
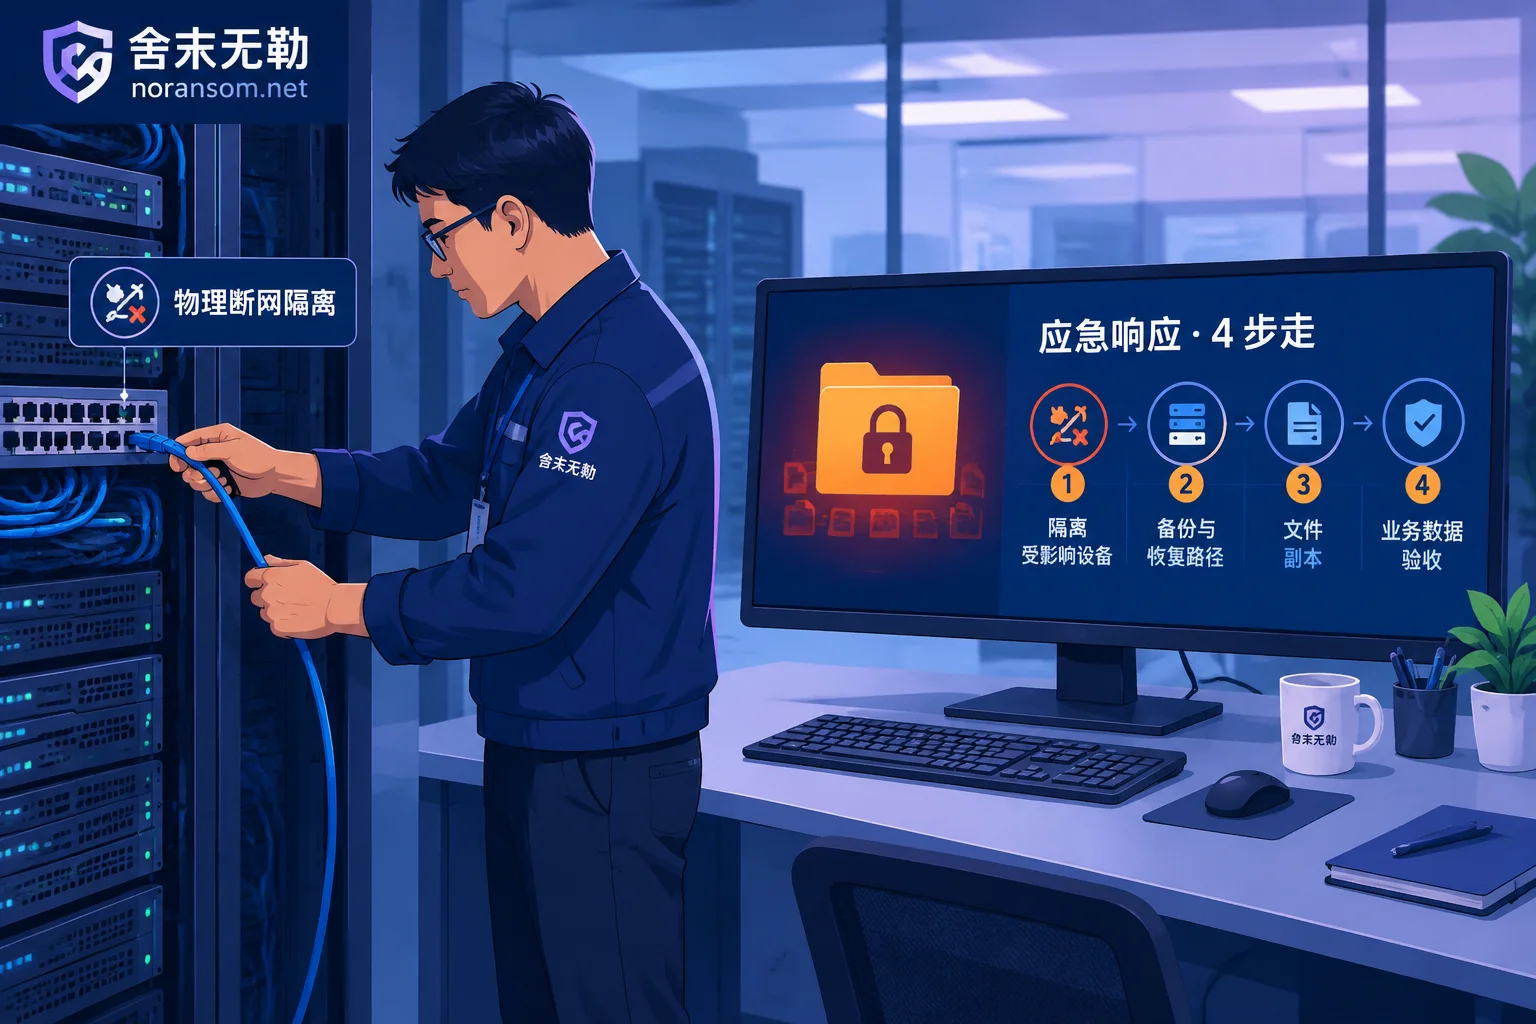
What to Do If You're Hit by Ransomware: A Complete Emergency Decision Checklist from the First 30 Minutes of Loss Control to Business Restoration
After discovering that your computer or server has been encrypted by ransomware, blindly restarting, running antivirus scans, or contacting the hackers often reduces the originally available data recovery space. This article is aimed at business leaders and IT operations staff, outlining a four-step standardized emergency response process: isolating the network and preserving the scene within the first 30 minutes, identifying the ransomware family, choosing between decryption and data extraction paths, and eradicating backdoors to rebuild defenses after cleanup.
Why Ransomware Victims Get Encrypted Again After Data Recovery: Recovering Data Is Only the First Step—Don't Go Live Until These Four Backdoors Are Cl
Many enterprises hit by Weaxor, Mallox, or Sorry ransomware painstakingly roll back from backups or finish database repairs, only to be re-encrypted within hours of going live. This article breaks down the four hidden causes of secondary infections (infected backups, unclosed initial entry points, persistent privileges, and internal lateral-movement jump hosts) and provides a complete pre-launch checklist for a safe return to production after recovery.
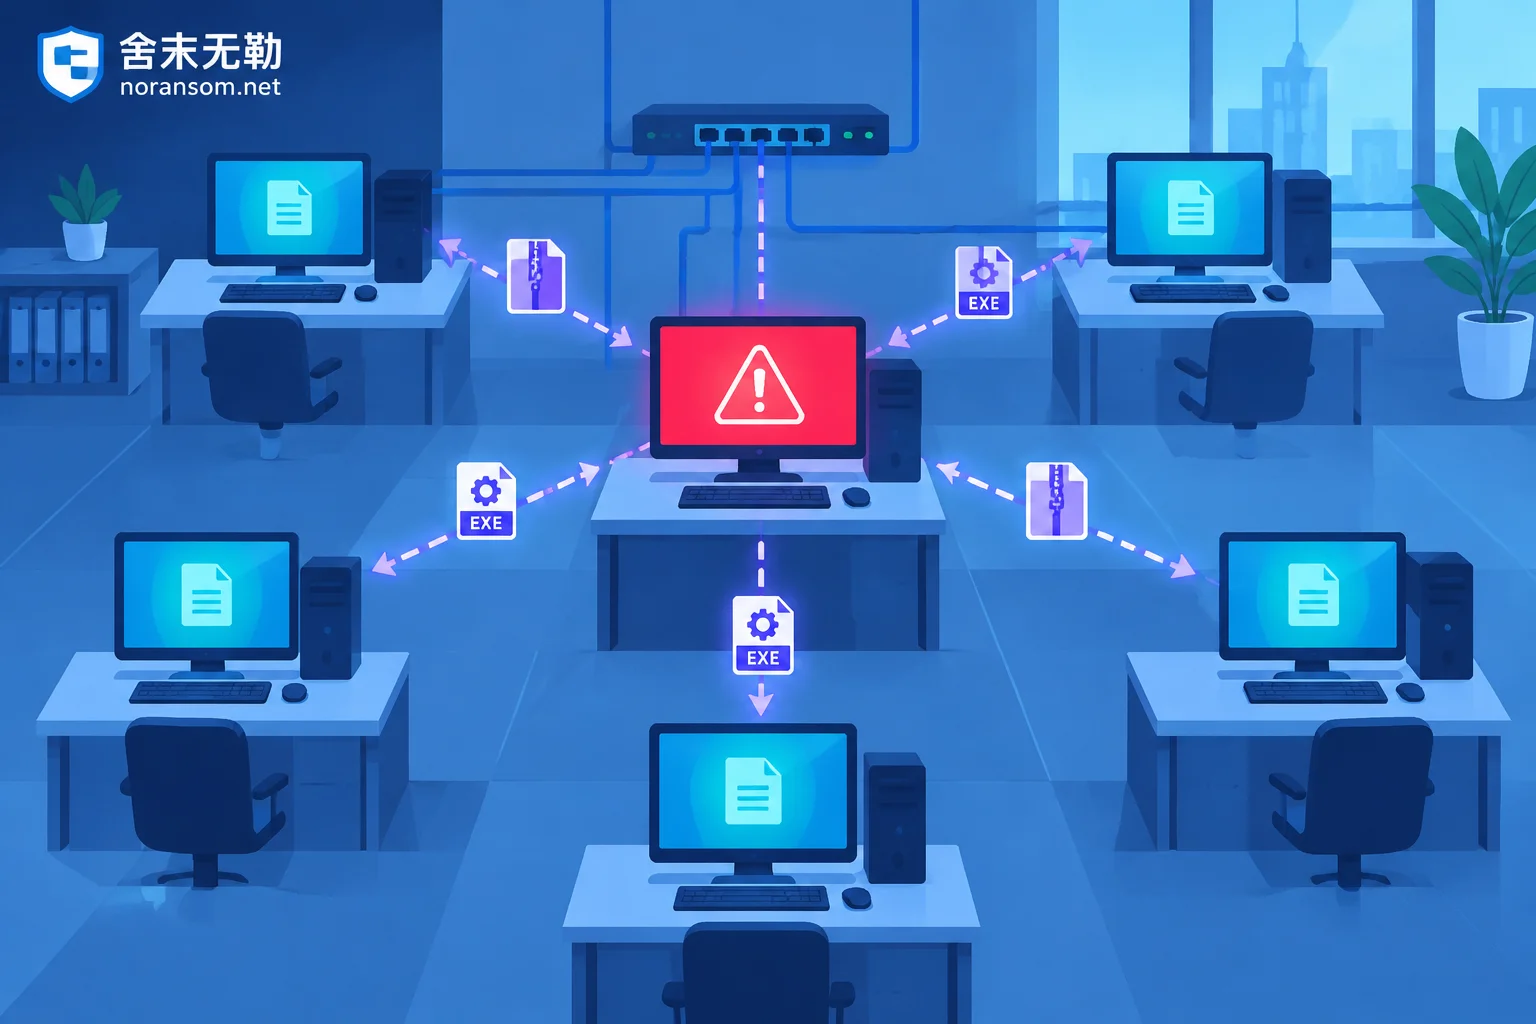
How to Investigate Other Office Computers After One PC Is Infected with the Silver Fox Trojan: First Obtain the Spread List, Then Check Each Machine f
The Silver Fox Trojan spreads in office networks mainly by taking over the victim's logged-in WeChat, DingTalk, QQ, and corporate email to send files to colleagues, not by scanning for intranet vulnerabilities. Therefore, the starting point for investigating other computers is to extract from the infected machine 'who was sent what file and when', then check each machine on the list for file drop traces, processes and security software status, and startup items, and handle host remediation, account sessions, and financial risks separately.
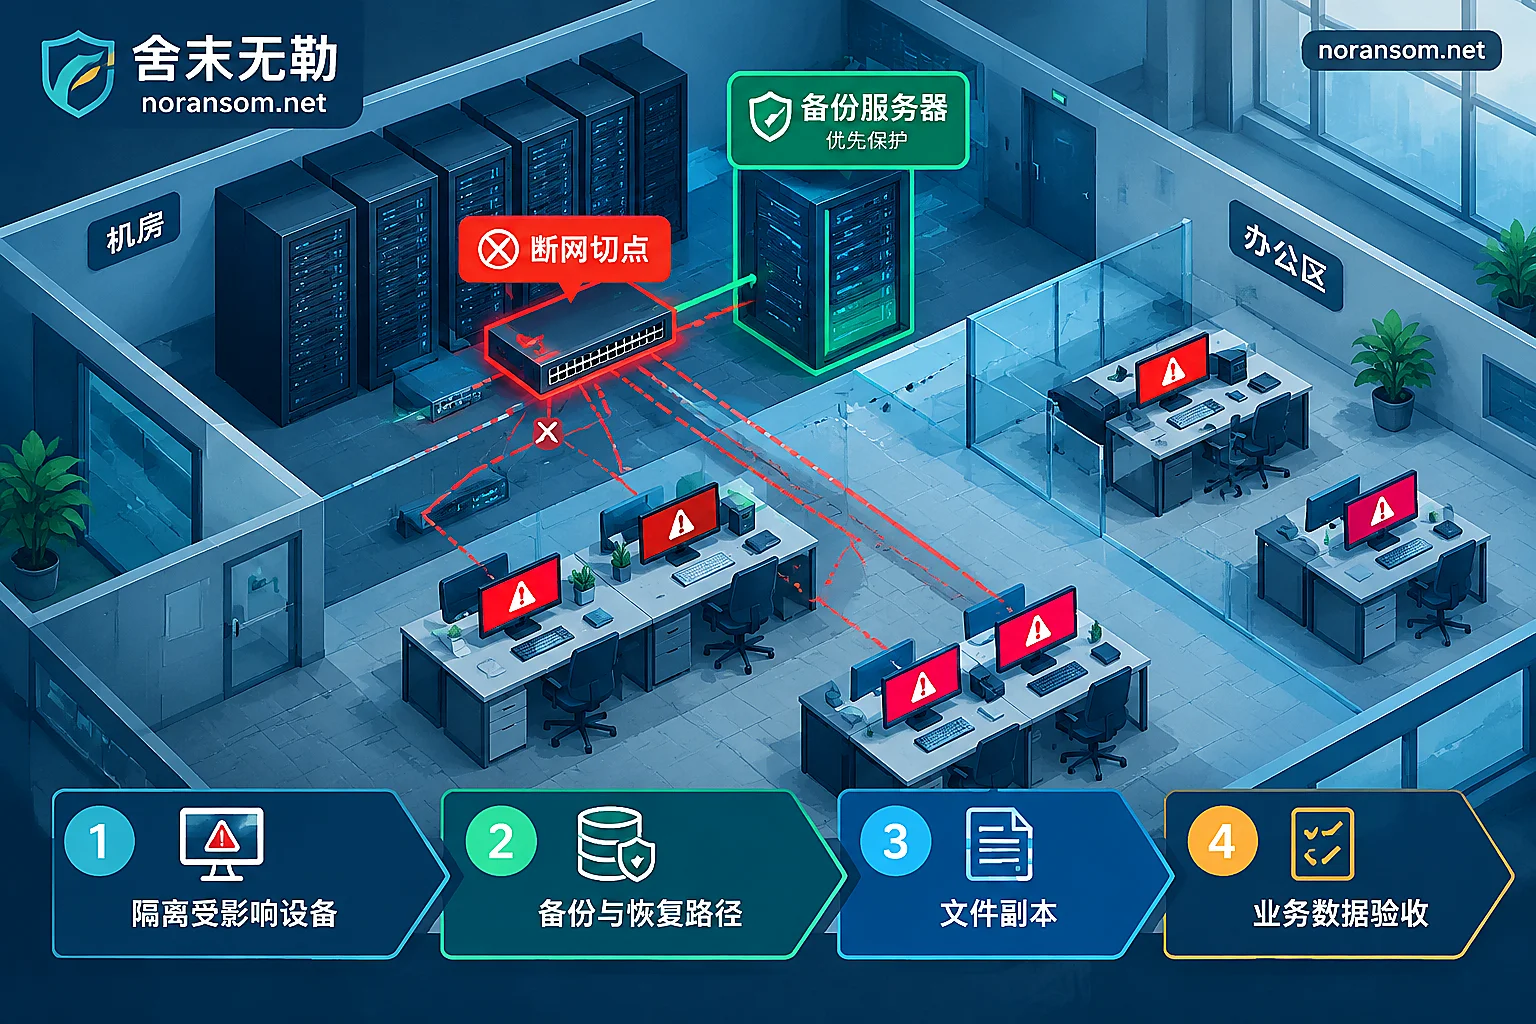
Multiple Computers Encrypted Simultaneously: Which to Handle First? Prioritize by Spread Risk, Not Urgency
When multiple machines on the internal network are hit by ransomware simultaneously, the order of response is not based on which machine has the worst damage, but on containing the spread, securing backups, cutting off the domain control and management plane, rescuing databases still being encrypted, and finally handling office computers that are completely locked. This article provides a four-level priority order, network disconnection methods for different network scales, trade-offs between shutdown and disconnection, and what must be preserved for each type of machine.


