Facing the "Encryption Threat": Why the More Urgent You Are, the Greater the Loss?
Entering 2026, ransomware attacks show stronger "precision strike" characteristics. Compared to the past wide-net approach, today's black market chains prefer targeted penetration into core business systems—especially databases, virtual machine clusters, and ERP financial software. Many enterprise IT operations staff, upon discovering business paralysis, instinctively restart servers, attempt to force-run encrypted software, or blindly search for so-called "one-click decryption packages."
However, these actions are exactly the "taboos" of data recovery. In many cases handled by Shemowule, the data that cannot be recovered is not due to strong encryption algorithms, but because subsequent secondary operations overwrote the originally recoverable fragments.
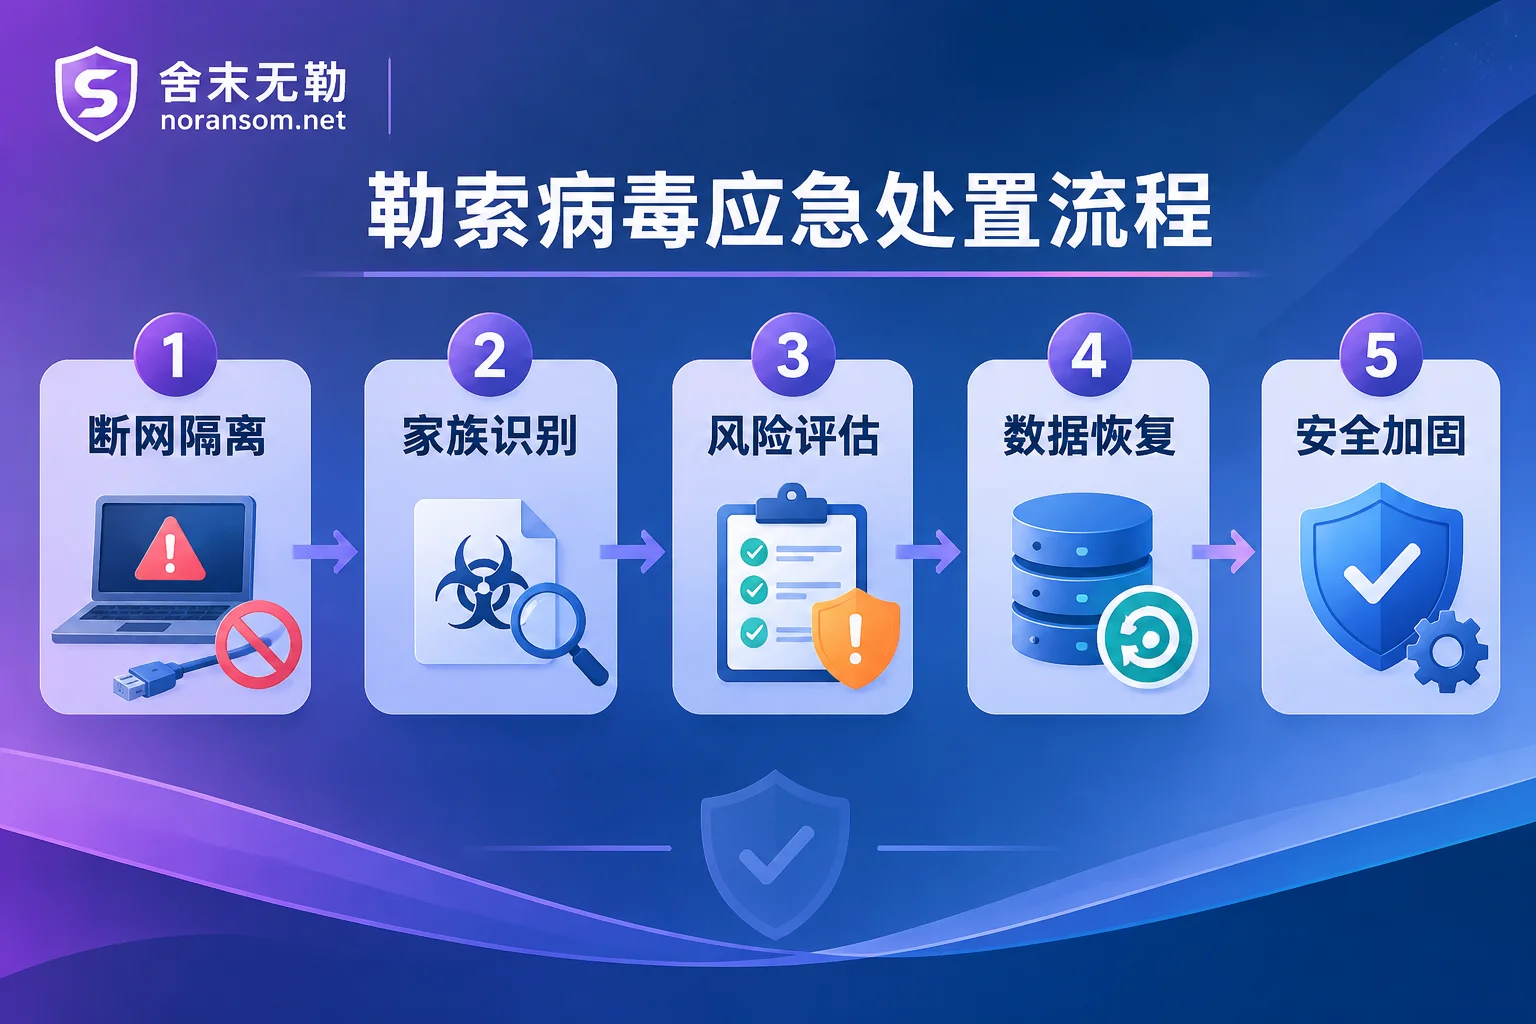
Scientific Emergency Response: The Golden Process Starting with "Stop-Loss"
When facing data encryption, the primary task is not "decryption" but "assessment."
- Ransomware Identification (Core First Step): Do not blindly try any tools without a clear family. Use online identification tools or compare with the suffix list to first lock down the attacker's identity. Different ransomware families (such as Weaxor, Mallox, etc.) have completely different encryption strengths and retention characteristics.
- Emergency Response and Isolation: If intrusion is detected, immediately execute 7×24 emergency response. Our expert team will assist you in controlling the impact at the first opportunity, removing residual Silver Fox Trojan backdoors, and preventing re-encryption during the recovery process.
Precise Rescue for ERP and Core Servers
When business is paralyzed, for ERP systems such as UFIDA, Kingdee, and Chanjet or ESXi/Hyper-V virtualization platforms, generic decryption tools often fail. Shemowule does not rely on a single "decryptor" but provides systematic solutions based on the environment:
- When direct decryption is not feasible: We proceed with backup and snapshot repair, database file-level repair, and extraction of unencrypted residual data. We mark data integrity by system and time point, ensuring delivery of a "runnable" business environment, not just damaged file fragments.
- Attack traceback and forensics: Not only save data but also clarify "where they came from." Through traceback and forensics services, we provide reports usable for compliance and reporting, and offer security hardening solutions to prevent repeated extortion.
Our Principle: Professionalism, Not Empty Promises
In the ransomware field, we insist on "no ransom payment, no negotiation with attackers." Because our core goal is to restore your productivity through technical means. Shemowule does not guarantee that all variants can be 100% decrypted, nor do we promise a fixed duration, because every piece of data deserves rigorous treatment.
If you are in the anxiety of a ransomware incident, please follow the scientific decision-making process:
- Identify first: Go to the virus database page to identify the family characteristics.
- Assess next: Through the assessment path, obtain a professional recovery feasibility conclusion.
- Recover last: Experts intervene and carry out rescue in a secure environment.
Do not push your data into the abyss in panic; stop first and assess the risk of each action.


Comments(0)