Recently, threat intelligence monitoring has shown that Lock3d ransomware is making a comeback, and the core databases of multiple enterprises have unfortunately been compromised, facing severe risks of business paralysis. This type of ransomware, with its high-intensity encryption methods and strict concealment capabilities, poses significant challenges to operations personnel.
I. Danger Signals of Lock3d Ransomware
Unlike previous ransomware attacks, Lock3d variants focus more on targeted attacks against enterprise databases (such as SQL Server, MySQL, etc.). Once infected, not only are file extensions tampered with, but core business data is often fully encrypted. When many enterprises discover the problem, their first thought is to "pay the ransom," but this is often the beginning of a mistake.
II. Refuse Blind Payment: A Scientific Emergency Path
When facing the situation of "database encrypted by ransomware," panic is the greatest enemy. Based on SheMoWuLe's years of frontline experience, we recommend that enterprises follow this scientific response process:
- Emergency stop-loss and isolation: Immediately disconnect the infected server from the network to prevent further encryption spread, while preserving on-site evidence. Unauthorized "system reinstallation" or "blind scanning and killing" are strictly prohibited.
- Professional family identification: Use the free identification tool or suffix query function to first confirm the infected family variant. Each virus has its unique encryption weaknesses, which are key to determining the subsequent plan. Check the ransomware database to learn about family characteristics.
- Recoverability assessment: Do not trust the hackers' promises; seek professional analysis of the underlying encryption logic. We provide targeted decryption and recovery assessment, looking for a breakthrough that does not require paying a ransom through low-level repair of file structures and database pages.
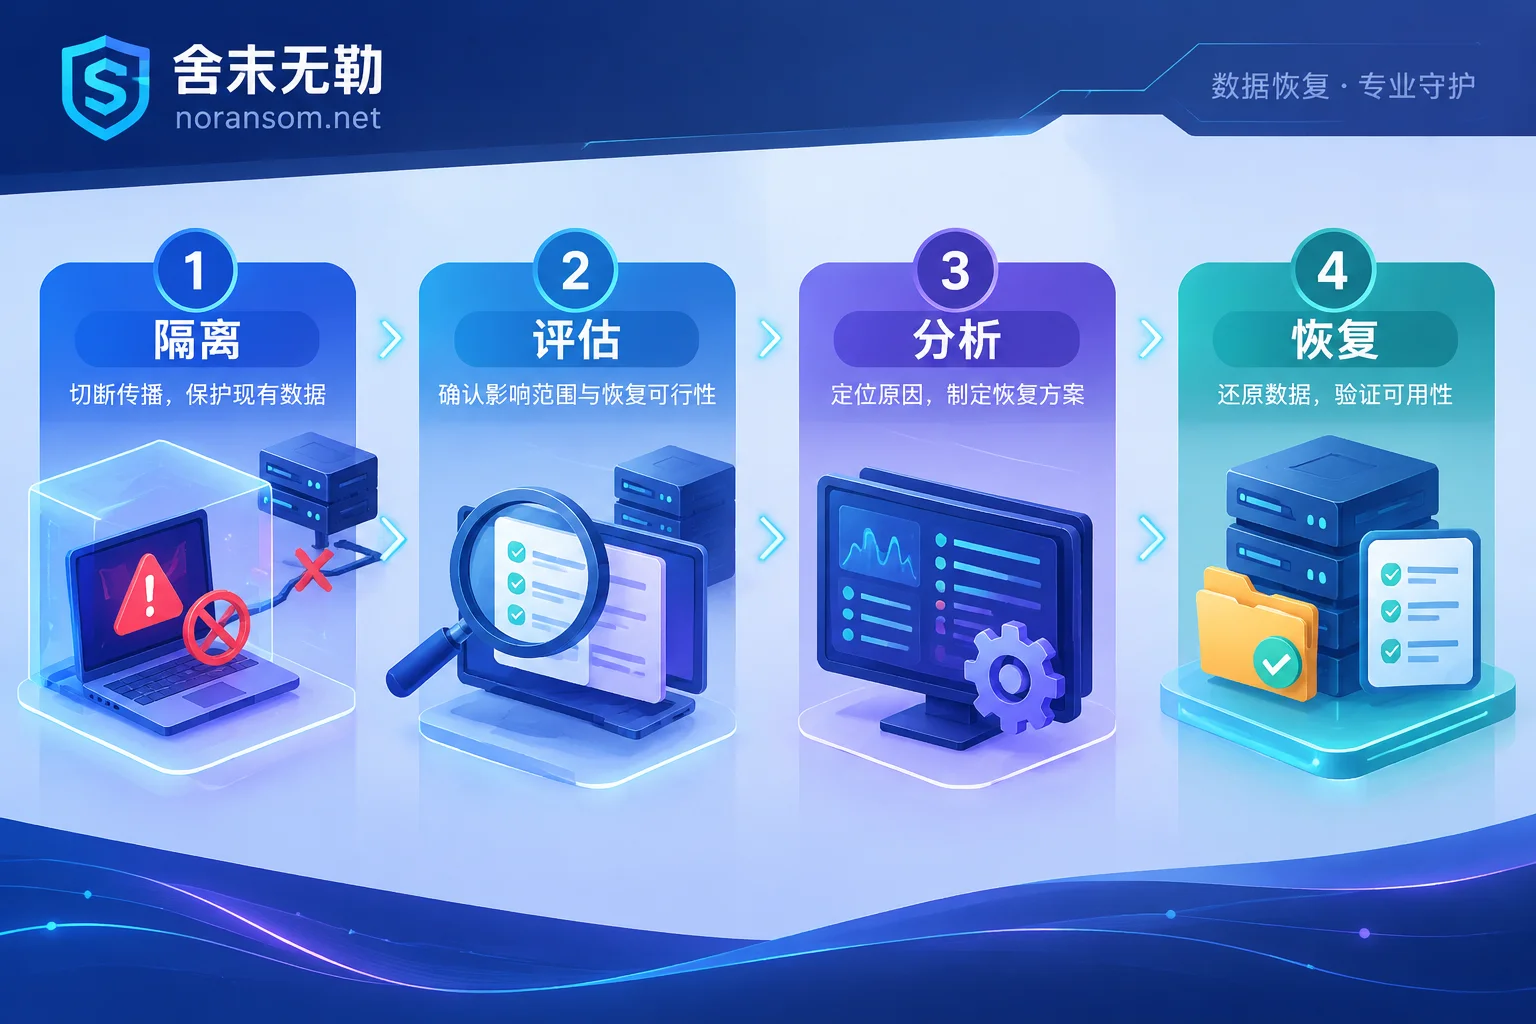
III. Comprehensive Response and Hardening: SheMoWuLe Solutions
When conventional decryption does not work directly, data recovery is the main focus. SheMoWuLe specializes in ransomware handling, providing one-stop services from data recovery, tracing and forensics to security hardening.
Especially in scenarios where ERP systems (such as Yonyou, Kingdee, Chanjet, etc.) are encrypted, we have accumulated rich experience and can develop personalized plans for different business scenarios to maximize the preservation of your production data.
Conclusion
There is no luck in cybersecurity; prevention is the best policy. But if you unfortunately fall victim, please respond calmly. Refusing to negotiate and choosing a professional path is the only way to protect your enterprise's core assets. If you are suffering from Lock3d or other ransomware intrusions, we recommend immediately referring to our emergency response process or contacting us through the contact page for professional support.


Comments(0)